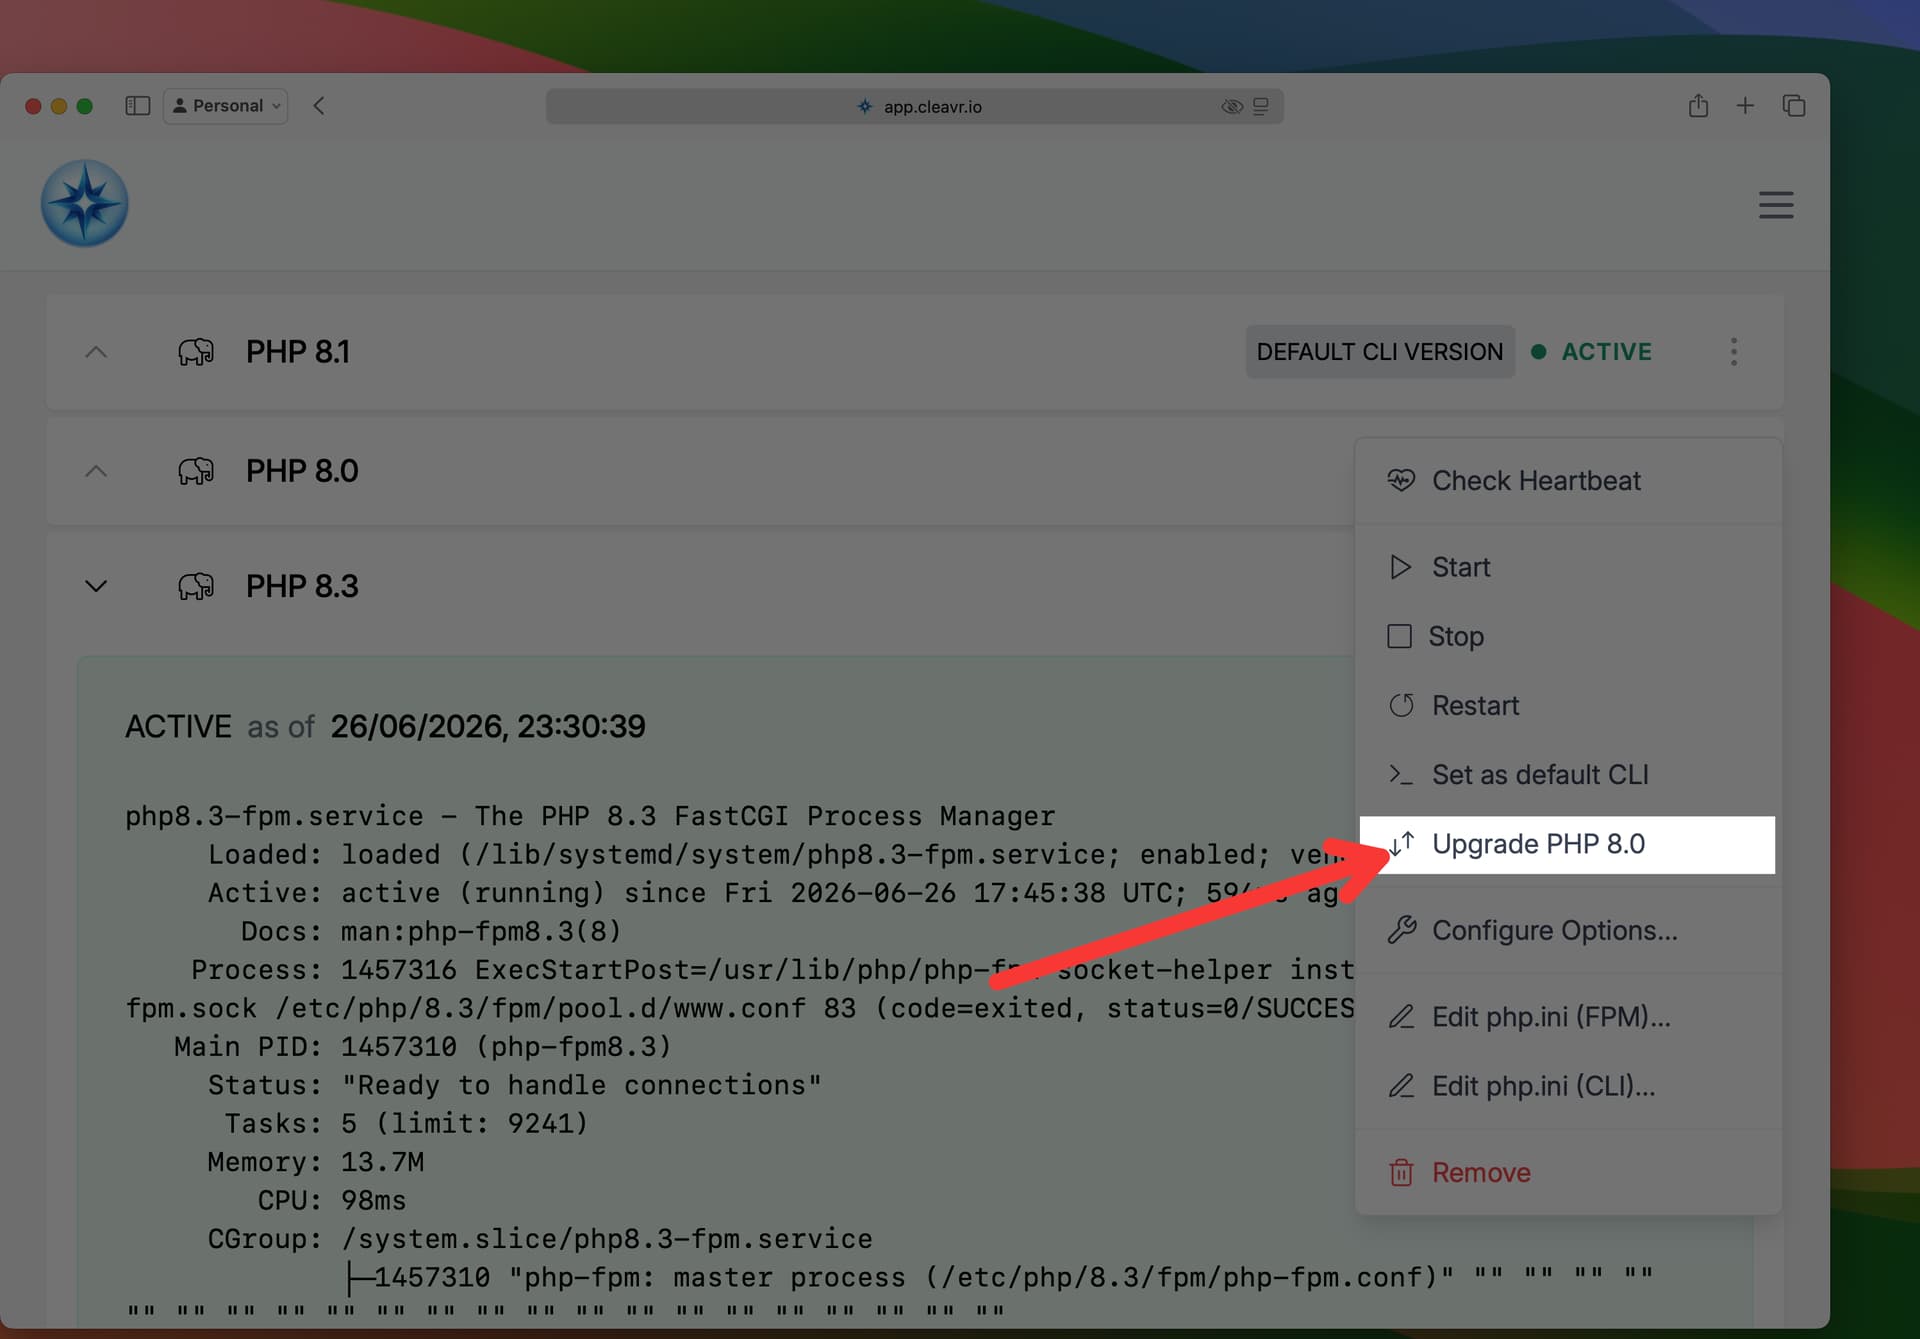
If the server is running old versions like PHP 7, install PHP 8.2 or newer from Services. The supported versions are 8.2, 8.3, 8.4, and 8.5. Then switch the site to that version in its PHP Settings.
A new PHP installation from the Services page already receives the fixed package.
If you upgraded a server from Ubuntu 20.04 to Ubuntu 22.04 and Cleavr can no longer connect to it, follow these steps to replace that server’s connection key with an ed25519 key.
If the server is inactive:
Open servers list page.
Click on the server status.
Click on the Update Connection Settings.
Expand Update Connection Key.
If the server is active:
Navigate to the server detail page, go to The Danger Zone, and open Connection Key.
On the Server:
Copy the command Cleavr shows.
SSH into the server as root with your own key.
Run the command. It adds the new public key.
Back in Cleavr
Click on Verify Key and Update.
Cleavr shows Server connection key updated and checks the connection again.
When the check succeeds, the server status should return to active.
PHP 8.4 stays on 8.4 and moves to the latest 8.4 release. The same applies to 8.2, 8.3, and 8.5. Sites using that PHP version can return a brief 502 while PHP-FPM restarts.
PHP 8.1 and older, and PHP 7, do not get the supported fix. Install PHP 8.2 or newer from Services, then switch the site in its PHP Settings.
Is there a way to have this functionality also for Node? Where you can update your node version to the newest minor upgrade? Seeing as node also was recently compromised. You can now only up- or downgrade to a major version.